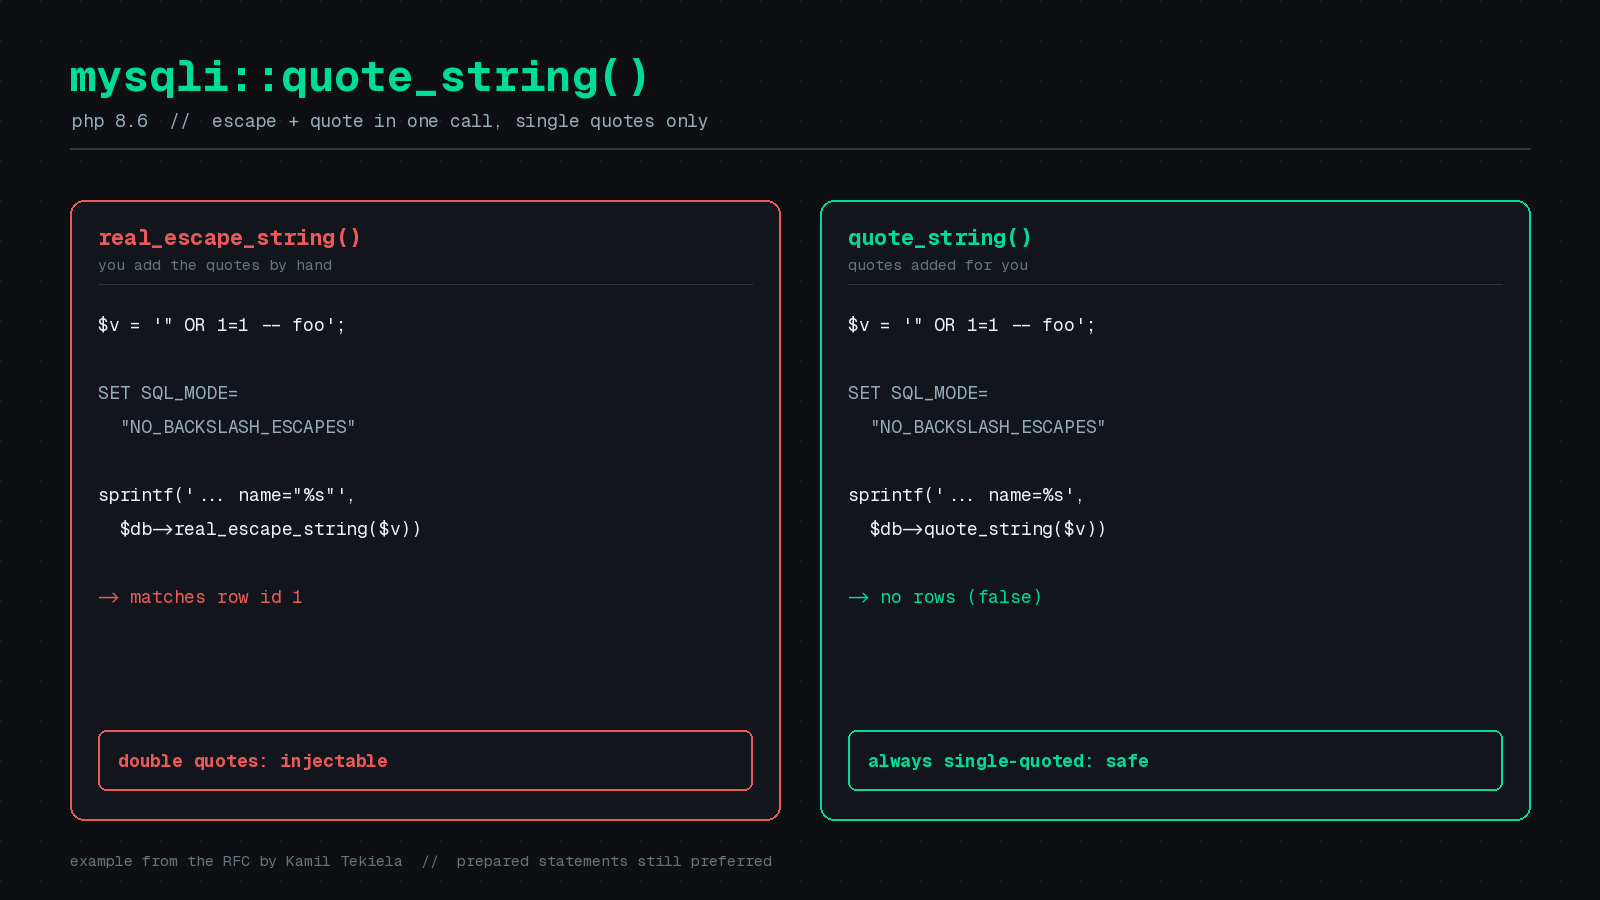
PHP 8.6 adds mysqli::quote_string(), a single-quote-only escaper modeled on PDO::quote(). See the injection gap it closes and how to migrate safely.
1 post tagged with "mysqli"
PHP 8.6 adds mysqli::quote_string(), a single-quote-only escaper modeled on PDO::quote(). See the injection gap it closes and how to migrate safely.